Enterprise security stories
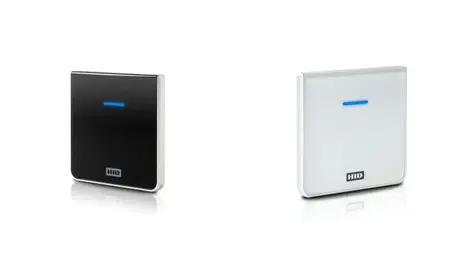
Architects and building operators get a flush-mounted reader that keeps access control discreet while supporting cards, mobiles and remote updates.
Strong demand for QNX helped lift BlackBerry's second-quarter profit and cash flow, prompting the company to increase full-year guidance.
Machine-generated requests now account for more than half of Fastly's network traffic, intensifying pressure to govern AI costs and security.
Security teams can now spot unsanctioned AI use across Windows estates, as Bitdefender adds risk ranking and policy controls to GravityZone.
Joint customers can now spot privileged identity risks alongside threat alerts in CrowdStrike Falcon, after BeyondTrust added new data feeds.
The service is aimed at firms that pay for Microsoft security tools but have yet to turn them into fully operational defences.
The hire comes as the identity security company passes USD $500 million in annual recurring revenue and faces sharper scrutiny on profitability.
Partner-led sales now account for Exabeam's highest-volume pipeline source, as new-logo business surged 138% above plan in the first half.
Passing USD $500 million in annual recurring revenue, the identity security group is adding public-company finance expertise as AI demand reshapes the market.
With exploit windows shrinking to under two days, AI could help Australian security teams decide what to patch first and cut delays.
Many firms still cannot stop AI agents from causing damage before execution, leaving systems exposed to production outages and data loss.
The update gives Microsoft 365, Google Workspace and Cisco Duo users faster containment and clearer evidence as identity attacks rise.
Enterprises could cut security sprawl as the platform extends one policy framework to users, devices and machines before login.
Attackers are exploiting AI faster than many defences can respond, prompting a shift to continuous testing for hidden exposures.
Targeted phishing and payment fraud are getting harder to spot as attackers mimic routine business workflows and trusted contacts.
Attackers are exploiting flaws before disclosure, leaving Australian organisations exposed for less time than patch cycles can keep up with.
Many organisations are still at an early stage of post-quantum adoption, with most only planning or testing quantum-safe cryptography.
The hire gives the cybersecurity firm a seasoned customer-facing adviser as enterprises grapple with more convincing phishing and impersonation attacks.
It cuts cabling and door-controller costs for US campuses, helping security teams manage locks centrally in older buildings and remote sites.
More than 12,000 inboxes were exposed as the kit used to bypass multi-factor authentication and sustain account access was taken offline.